Protect privileged access across your entire environment with agentless, identity-based controls built for resilience, rapid deployment, and high-stakes environments.
BeyondTrust Competitors: Xage XPAM vs. BeyondTrust
Traditional PAM Complexity Can Create Security Gaps
When evaluating BeyondTrust competitors, one key consideration is how easily privileged access protection can extend across the entire environment. PAM architectures that require multiple products, gateways, vaults, and management interfaces can add complexity, especially across distributed, legacy, or disconnected assets alongside traditional IT. According to the 2026 Verizon Data Breach Investigations Report, credential abuse remains an initial access vector in 13% of breaches.
BeyondTrust separates capabilities across Password Safe, Privileged Remote Access, and Endpoint Privilege Management. Xage takes a different approach, bringing privileged access, remote access, MFA, session controls, and identity-based enforcement together through a distributed architecture.
What Is Xage Extended Privileged Access Management?
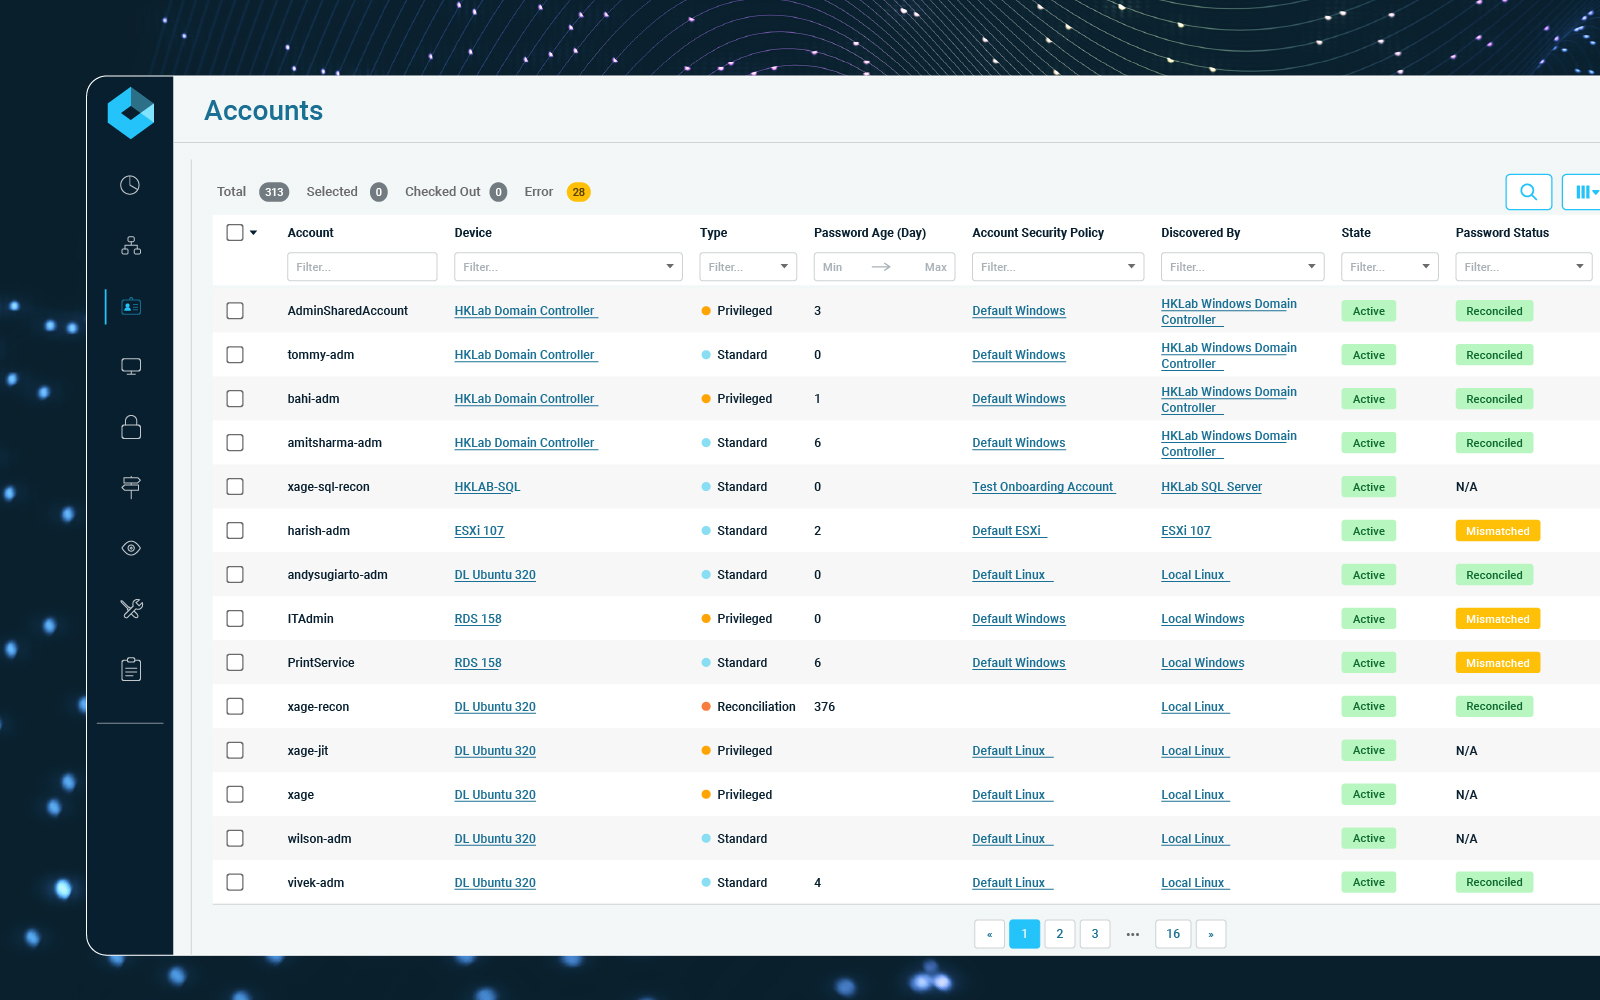
Xage Extended Privileged Access Management (XPAM) is an identity security solution that controls and audits privileged access across human and non-human identities without relying on a centralized enforcement architecture.
Xage combines privileged account discovery, credential protection, just-in-time access, MFA, session management, secure remote access, and identity-based controls in one platform.
With Xage XPAM, you can:
- Apply privileged access controls without deploying agents across every endpoint.
- Replace standing privilege with just-in-time, policy-based access.
- Extend MFA to legacy systems and resources that do not natively support it.
- Control and record privileged sessions across IT, OT, cloud, and distributed environments.
- Maintain local authentication and policy enforcement when WAN or cloud connectivity is unavailable.
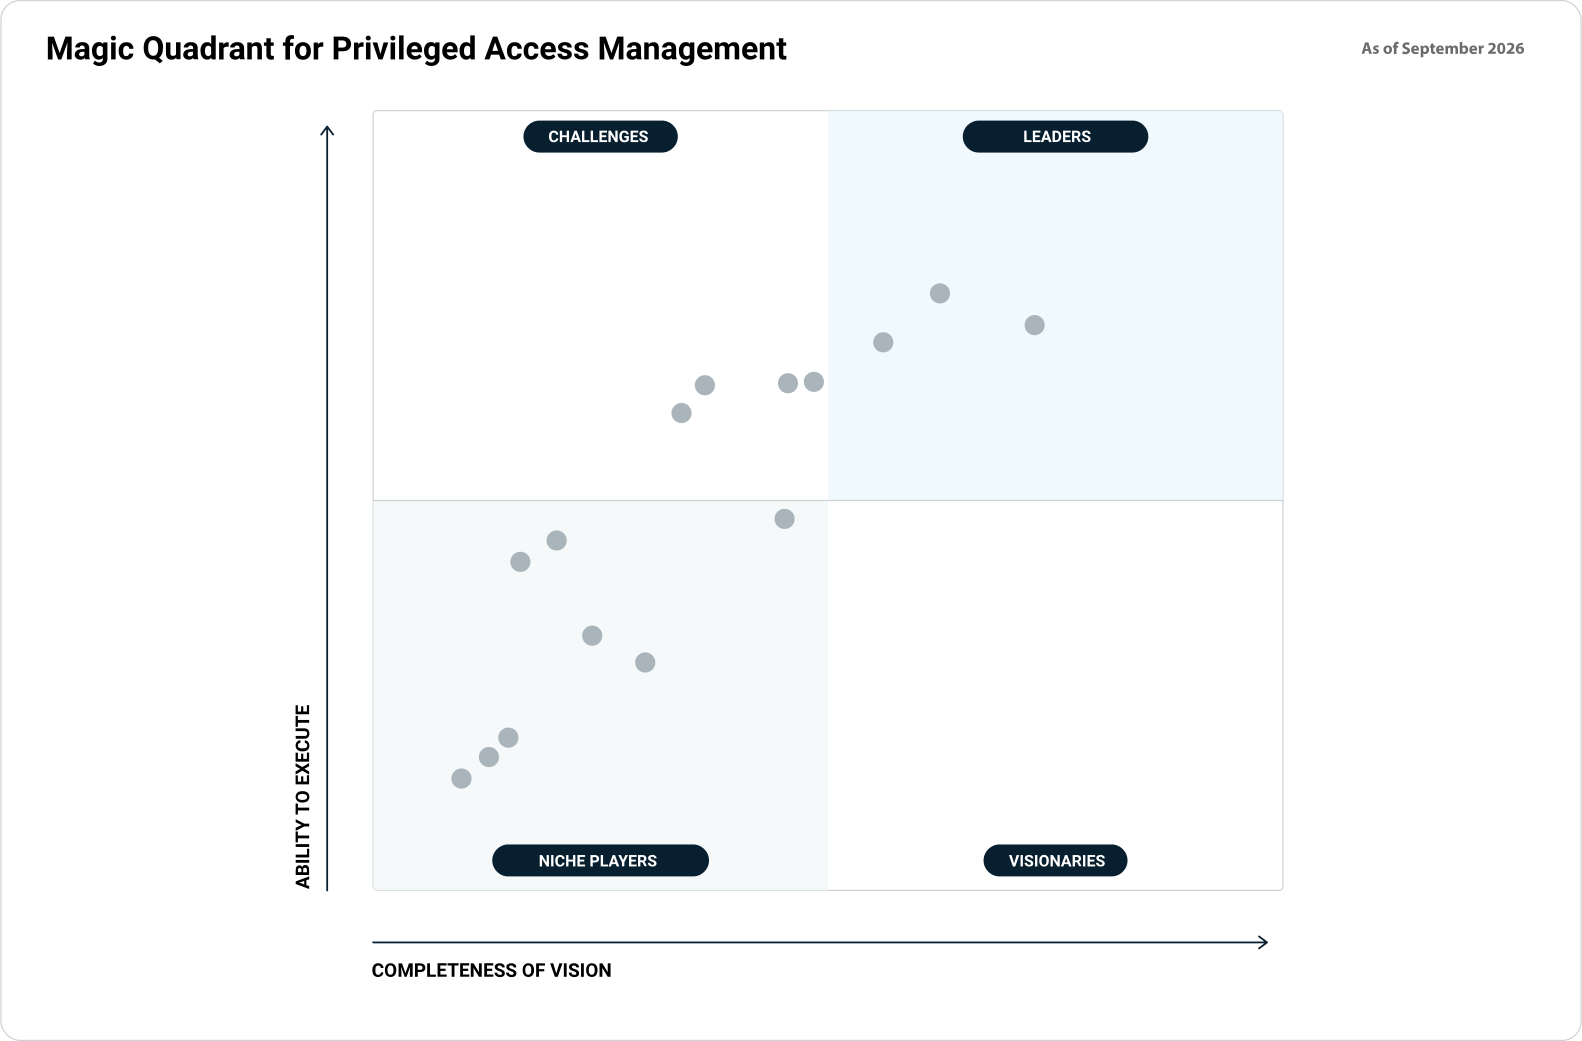
There’s a New Name in PAM.
Xage Security Named in the 2026 Gartner® Magic Quadrant™ for Privileged Access Management
Read the Report
BeyondTrust Competitors: At-a-Glance Comparison
Xage XPAM and BeyondTrust both address privileged access, but they take different architectural approaches. Xage uses a distributed Zero Trust Fabric and consolidates privileged access and related identity controls, while BeyondTrust provides PAM capabilities across multiple product lines.
| Criteria | Xage XPAM | BeyondTrust |
|---|---|---|
| Core architecture | Distributed fabric (Xage Fabric); no central vault | Centralized, vault-based (Password Safe) |
| Core components for full capability | 2 (Manager + Nodes) | 5+ components |
| Fully self-hosted, no cloud dependency | Yes, incl. remote access & ZTNA | On-prem/appliance supported; SaaS elements need internet |
| Native OT/ICS/SCADA support | Yes, incl. Purdue Model alignment | Not purpose-built for OT |
| Zero Trust Remote Access | Native, included | Separate product line (PRA) |
| Typical time to initial protection | Hours to about a day | Weeks to months (multi-component) |
| On-prem / distributed sites | Yes, supports on-prem and distributed sites, even if connectivity is disrupted | Primarily SaaS delivery model. Requires additional jumpbox infrastructure, server licenses, and central connectivity to remain operational. |
| Licensing model | User-based, unlimited assets, one tier | User + component/module based |
| Multi-user session collaboration | Supported natively | Limited |
Full Comparison: Xage XPAM vs. BeyondTrust
Xage XPAM and BeyondTrust differ across privileged access architecture, credential security, session management, deployment, resilience, identity controls, and infrastructure requirements. The detailed comparison below shows how each approach addresses these areas.
Download as PDF
Privileged Access Security & Management
Xage XPAM takes a different approach to privileged access security by applying controls immediately through an agentless policy overlay, without waiting for every credential to be discovered and vaulted. It combines decentralized credential protection, just-in-time access, resilient local enforcement, and secure third-party access to reduce standing privilege and protect access across distributed environments.
| Criteria | Xage XPAM | BeyondTrust |
|---|---|---|
| Discovery & Time-to-Protection | Instant Agentless Policy Overlay: Governs access immediately upon network placement; no need to wait for full credential discovery/rotation. | Automated Account Discovery: Discovers unmanaged local/domain accounts and service accounts across Windows/Active Directory |
| Credential Management & Vaulting | Decentralized / Secrets-First: Eliminates standing credentials; supports dynamic rotation, vaulted secrets, and credential injection without exposing plaintext to users. | Centralized Vault (Password Safe): Rule-based auto-discovery and rotation stored in appliance/cloud vault database. |
| Vault Security | Quantum-resistant cryptography: credentials and policy are fragmented and distributed across the Xage Fabric, so no single node holds a complete secret. | AES-based encryption; no public documentation of post-quantum cryptograph |
| Resilience | No single point of failure; one node compromised does not expose credentials or policy. 100% Resilient Local Enforcement Nodes sync cryptographically; full authentication and policy enforcement continue during WAN/cloud outages. | Vault availability is central to the architecture; HA configurations reduce but don't eliminate this dependency |
| Zero Standing Privilege (ZSP) & JIT Access | Native JIT Protocol Proxy: Ephemeral access granted at the protocol/asset level; dynamic role-binding; zero persistent local admin rights. | Time-Bound Ephemeral Access (Entitle integration): On-demand approval workflows and access elevation; tied to Password Safe/PRA. |
| Third-Party & Remote Vendor Access | Direct Agentless Zero Trust Overlay: Browser-based or native client access to internal assets; no client VPN, no jump hosts, no network-level exposure. | Dedicated Appliance (PRA / Remote Support): Industry standard for vendor portals; requires maintaining internet-facing gateways. |
Session Management & Security Features
Xage integrates privileged session controls with the same platform used for remote access and policy enforcement. BeyondTrust provides session capabilities through its PAM and remote-access product lines.
| Criteria | Xage XPAM | BeyondTrust |
|---|---|---|
| Command/process capture | Agentless SSH command capture and RDP process capture | Available; some capture scenarios rely on an installed agent |
| Session recording | Built-in, agentless | Built-in, agentless |
| Zero Trust Remote Access | Native, included in the same platform | Delivered via Privileged Remote Access / Remote Support, separate product lines within the Pathfinder platform |
| Session collaboration | Multiple users can join the same session concurrently | Limited multi-user session collaboration |
| Secure file transfer with malware scanning | Built-in, with AV integration, fingerprinting, and integrity checks | Not natively supported |
| East-west (machine-to-machine) control | Policy-based control of lateral M2M traffic | Not a core PAM capability |
Deployment & Infrastructure Footprint
Xage uses distributed enforcement nodes rather than relying on a single centralized enforcement point. This architecture is designed to extend privileged-access controls to distributed and disconnected environments while minimizing network and firewall changes.
| Criteria | Xage XPAM | BeyondTrust |
|---|---|---|
| Architectural Model | Distributed Zero Trust Mesh · Tamper-proof, multi-node consensus · Zero single point of failure | Appliance / Gateway Clusters; Dedicated hardware/VM gateways; vulnerable network entry points |
| Deployment model | Software-based; Ubuntu/RedHat VM or virtual appliance | Available as software (Windows-based), virtual appliance, or physical appliance |
| Core components | Minimum 2 (Manager + Nodes) for full capability | Full Total PASM suite (Password Safe + Privileged Remote Access + supporting services) typically involves 5 or more components |
| Agent requirement | Agentless | Agentless for core PASM; HTTP/HTTPS application access is typically proxied through a jump-server-style component |
| Air-gapped/offline support | Fully self-hostable, no cloud dependency, including ZTNA and remote access. 100% operational when WAN, cloud, or central services are disconnected. | On-prem/appliance deployment supported; SaaS-delivered elements and routine product updates typically depend on internet connectivity |
| Centralized management | Single console for PAM, ZTNA, MFA, SSO, file transfer, and session collaboration | Separate consoles across Password Safe, Privileged Remote Access, and Endpoint Privilege Management |
| Network/firewall changes | Outbound-only, unidirectional tunnels between nodes; minimal rule changes | Session proxying and jump-server components typically require broader network and firewall configuration |
Identity & Access Control
Xage extends identity-based policy enforcement beyond traditional administrator accounts and can apply MFA and access controls to resources that lack native identity security capabilities.
| Criteria | Xage XPAM | BeyondTrust |
|---|---|---|
| AD/LDAP integration | Supported, including multi-level LDAP/LDAPS | Supported |
| Identity-based micro-segmentation | Supported via Xage enforcement points | Not a core PASM capability |
| Universal MFA Support | Universal MFA Injection: Integrates with Entra ID, Okta, Ping; injects MFA into legacy IT/OT systems, protocols, and devices that lack native MFA support. | Gateway Portal Dependent MFA required to enter PRA portal; internal direct connections lack MFA enforcement. |
Scalability & Resilience
Xage distributes authentication and policy enforcement so protected environments can continue enforcing access controls during WAN, cloud, or central-service outages.
| Criteria | Xage XPAM | BeyondTrust |
|---|---|---|
| Installation time | Containerized install; operational in hours | Multi-component install; Gartner notes customer feedback identifies initial setup and configuration as more complex and time-consuming than some competitors |
| HA model | Built-in fault tolerance via distributed consensus | HA supported via clustered/appliance configurations, adding architectural complexity |
| Patching/upgrades | Rolling updates across distributed nodes | Sequential upgrade path across vault and dependent components |
| Blast Radius Containment | Asset-Layer Isolation: Compromise of one node or credential cannot compromise the rest of the estate | Severe risk with public-facing PRA/Remote Support appliances that are proven targets for RCE zero-days. |
Licensing & Total Cost of Ownership
Xage uses user-based licensing with unlimited assets and a two-component core architecture. The goal is to reduce the additional infrastructure, product modules, and management overhead required to extend PAM across an enterprise.
| Criteria | Xage XPAM | BeyondTrust |
|---|---|---|
| Infrastructure Overhead (TCO) | Zero Appliance Sprawl: Eliminates RDP jump boxes, dedicated bastions, hardware appliances, and VPN licensing. | Fragmented with separate architectures and consoles for Password Safe, PRA, and EPM (disparate acquisitions). |
| Day-One Protection & Time-to-Value | Immediate (Hours to Days) Agentless overlay wraps any asset with JIT access & MFA instantly, without prior vaulting. | Multi-Month Rollout Requires standing up appliance pairs, configuring gateways, and deploying desktop EPM agents. |
| License model | User-based, unlimited assets, single tier | Combination of user-based and per-component/module licensing across product lines |
| Cost | Lower infrastructure overhead due to a 2-component architecture | Gartner's Oct 2025 PAM Magic Quadrant notes BeyondTrust's overall software pricing remains above the market average despite bundle discounts introduced with its Pathfinder Essentials/Plus/Flex tiers |
User Experience
Xage consolidates privileged-access workflows within a single management experience and policy model, reducing the number of separate interfaces administrators need to manage.
| Criteria | Xage XPAM | BeyondTrust |
|---|---|---|
| Admin experience | Single console, unified workflows | Customer feedback identifies UI and navigation as an improvement area |
| Learning curve | Low – fewer moving parts, one policy model | Higher across multiple modules, each with distinct configuration logic |

“We rely on experts like Xage Security to protect and secure our critical infrastructure. Xage provided us with an innovative approach to cyber harden OT and IT infrastructure as well as help us meet regulatory requirements.”
– Mark Huse, Chief Information Officer, Kinder Morgan

Xage protects privileged access in environments where security controls cannot depend on uninterrupted cloud or WAN connectivity.
Kinder Morgan uses Xage to secure privileged access across approximately 3,000 servers and 400 administrators in its data center environment. With MFA and just-in-time, just-enough access in place, the company reduced related support tickets by 46%.
Read the Case Study
Frequently Asked Questions
What Is the Difference Between Xage XPAM and BeyondTrust PAM?
Xage XPAM uses a distributed Zero Trust architecture and combines privileged access, remote access, MFA, session controls, and identity-based enforcement. BeyondTrust provides privileged access capabilities across multiple product lines, including Password Safe, Privileged Remote Access, and Endpoint Privilege Management.
Is Xage XPAM an Alternative to BeyondTrust?
Yes. Xage XPAM provides privileged account discovery, credential management, JIT access, session management, secure remote access, MFA, and auditing for organizations evaluating alternatives to BeyondTrust PAM.
Can Xage XPAM Work Without Cloud Connectivity?
Yes. Xage XPAM can be fully self-hosted and is designed to continue local authentication and policy enforcement when WAN, cloud, or central services are unavailable.
Does Xage XPAM Support OT and Legacy Systems?
Yes. Xage uses an agentless architecture and can extend privileged access and MFA controls to legacy IT and OT systems, protocols, and devices, including resources that lack native MFA support.
How Does Xage XPAM Reduce Standing Privilege?
Xage uses just-in-time access to grant ephemeral privileges at the protocol or asset level. Access can be dynamically authorized based on policy without maintaining persistent local administrator rights.
See How Xage XPAM Compares
Discover how Xage can simplify privileged access management, extend identity-based controls across your environment, and protect human, machine, and AI identities.